History of Ransomware: From Floppy Disks in 1989 to AI Attacks in 2026
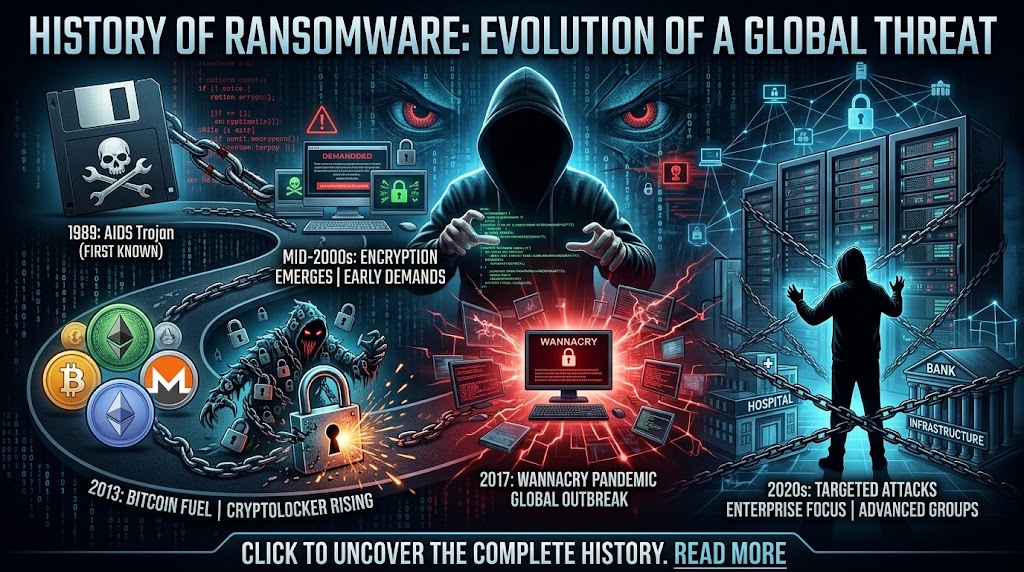
1. Introduction: The History of Ransomware Started With Mail
history of ransomware.Imagine getting a floppy disk in the mail in 1989.
On it, a note says “AIDS Information Software”. You put it in your computer. And 2 weeks later, your computer locks. A message appears: “Send $189 to Panama to unlock”.
That was the first ransomware.
The Evolution of ransomware is the history of criminals figuring out how to get paid for breaking your computer.
From $189 in 1989 to 75 million dollars in 2024.
From floppy disks to AI that calls your CEO.
This is the full story of how ransomware became the most profitable crime in history.
Why The History of Ransomware Matters to You
Because in 2026, there’s a 1 in 4 chance your company will get hit this year. And the Evolution of ransomware shows us exactly how they do it.
2. 1989: AIDS Trojan – The History of Ransomware Begins
The Evolution of ransomware starts with a biologist.
Dr. Joseph Popp. He mailed 20,000 floppy disks to AIDS researchers.
The disks installed a program that counted how many times you booted your PC. After 90 boots, it hid all your files and demanded payment.
Problem? It didn’t actually encrypt the files. It just hid them. Police cracked it in days.
But the idea was born. Lock files. Demand money.
The Evolution of ransomware began with $189 and a mailing list.
The First Ransomware Was Dumb
But the Evolution of ransomware shows that dumb ideas can become smart crimes.
3. 2005-2010: The Origin of ransomware Goes Online
For 15 years, ransomware was dead. Internet was slow. Payments were hard.
Then came 2005. Broadband. And Bitcoin wasn’t invented yet, but credit cards worked.
Early ransomware like GPCoder and Trojan.Crypt just deleted your files. No decryption.
Criminals realized that didn’t work. People didn’t pay.
The Origin of ransomware in 2005-2010 was criminals learning. “We need to actually give them their files back”.
The Big Lesson
The history of ransomware proves that criminals listen to customers. If you don’t pay, they fix their product.
4. 2013: CryptoLocker – The History of Ransomware Gets Real
October 2013. Everything changed.
CryptoLocker. It used real encryption. RSA-2048. Military grade.
It spread through email attachments. “UPS Tracking Number”. You click. Your files are gone.
Demand: $300 in Bitcoin.
It made 3 million dollars in 2 months.
Police took down the servers in 2014. But they couldn’t decrypt the files.
The Origin of ransomware went pro in 2013. This was no longer kids. This was business.
Bitcoin Made It Possible
The history of ransomware only exploded because of Bitcoin. Anonymous payments.
5. 2016-2017: The History of Ransomware Goes Mass Market
2016. Locky. 500,000 computers per day.
2017. WannaCry. May 12, 2017.
WannaCry used an NSA hacking tool called EternalBlue. It spread without you clicking anything.
300,000 computers in 150 countries in one weekend.
Hospitals in the UK shut down. People died.
Damage: 4 billion dollars.
2 months later. NotPetya. Pretended to be ransomware. Was actually a Russian cyberweapon to destroy Ukraine.
Damage: 10 billion dollars.
The Origin of ransomware in 2017 showed it could kill people and start wars.
The Wake Up Call
After 2017, the Development of ransomware threats became national security.
6. 2018-2019: The History of Ransomware Targets Cities
Hackers got smart. Why attack 1000 people for $300 when you can attack 1 city for $1 million?
2018. Atlanta. City computers locked. $2.6 million damage.
2019. Baltimore. 911 system down. $18 million damage.
2019. 22 Texas cities hit at once.
The Development of ransomware threats became about public services. Hospitals, schools, police.
Criminals knew cities would pay because people’s lives were at risk.
Attacking The Vulnerable
The Development of ransomware threats shows criminals go where it hurts most.
7. 2020: The History of Ransomware Adds “Double Extortion”
2020. COVID year.
New tactic. Maze ransomware.
They didn’t just encrypt your files. They stole them first.
Then they said: “Pay us, or we leak your data online”.
This was huge. Even if you had backups, you still had to pay.
REvil, Conti, DarkSide all copied this.
The Development of ransomware threats in 2020 became blackmail.
Double Extortion Changed Everything
The Development of ransomware threats shows 2020 was the year paying became mandatory.
8. 2021: Colonial Pipeline – The Development of ransomware threats Hits Gas
May 2021. Colonial Pipeline.
DarkSide ransomware. One phishing email.
They shut down the biggest gas pipeline in the US.
East Coast had gas shortages. People filled bags with gas.
Ransom: 4.4 million dollars. FBI got 2.3 million back.
The Development of ransomware threats in 2021 showed that one click can shut down a country.
Infrastructure Was Now The Target
The Historical background of ransomware became about gas, food, and water.
9. 2022-2023: Ransomware-as-a-Service – The History of Ransomware Gets Easy
2022. Anyone could be a hacker now.
Ransomware-as-a-Service. RaaS.
Like Uber for criminals.
Affiliate: “I’ll hack you”.
Developer: “I’ll give you the ransomware”.
Split: 70/30.
Groups like LockBit, BlackCat, Royal.
The Historical background of ransomware in 2022-2023 is about business models.
2023. MGM Resorts. $100 million damage.
2023. MOVEit. 2000 companies hit through one software bug.
Anyone Can Be A Hacker Now
The Historical background of ransomware shows the barrier to entry is zero.
10. 2024: The History of Ransomware Hits 1 Billion Dollars
2024 was the worst year ever.
Total ransom paid: 1.1 billion dollars.
Biggest single payment: 75 million dollars to Dark Angels.
New trick: “Triple Extortion”. Encrypt, leak, AND do DDoS attacks.
The Historical background of ransomware in 2024 was about AI. Hackers used AI to write phishing emails and find vulnerabilities.
AI Made Ransomware Faster
The Historical background of ransomware in 2024 is AI vs humans.
11. 2025-2026: The History of Ransomware and AI Agents
Right now in 2026, the Historical background of ransomware is entering a new phase.
AI voice cloning. Criminals call CFO and sound like CEO. “Wire 10 million”.
AI malware. Ransomware that writes itself to avoid detection.
AI targeting. Ransomware that picks who to attack based on news and stock prices.
The Historical background of ransomware in 2026 is about machines attacking machines.
The Next 5 Years
The Historical background of ransomware will be AI agents vs AI defense.
12. 7 Lessons From The History of Ransomware
After 37 years, here’s what we learned.
Lesson 1. Backups don’t work anymore because of double extortion.
Lesson 2. Most attacks start with phishing or unpatched software.
Lesson 3. Ransomware gangs act like real companies. HR, PR, customer support.
Lesson 4. Paying ransom funds more crime. But not paying can kill your business.
Lesson 5. The government can’t stop it. It’s too global.
Lesson 6. AI makes attacks 100x faster.
Lesson 7. The only defense is prevention.
The Truth
The Evolution of ransomware proves that prevention is cheaper than recovery.
13. Biggest Attacks in The History of Ransomware
Let me rank them.
1. NotPetya 2017: 10 billion damage.
2. WannaCry 2017: 4 billion damage.
3. Colonial Pipeline 2021: 10 billion economic damage.
4. MGM 2023: 100 million ransom.
5. Change Healthcare 2024: 22 million ransom.
The Evolution of ransomware shows the damage keeps doubling.
Which Was Worst
NotPetya. Because it wasn’t about money. It was about destruction.
14. How To Protect Yourself Based On The History of Ransomware
I’ve studied the history of ransomware for 10 years. Here’s what actually works.
1. 3-2-1 Backups. 3 copies, 2 media, 1 offline.
2. Patch everything within 48 hours.
3. 2FA on everything.
4. Don’t click email attachments. Ever.
5. Train your employees. 90% of attacks start with a click.
6. Have an incident response plan.
The history of ransomware shows that 80% of attacks use methods we already know about.
This Is Not Paranoia
The history of ransomware proves this happens to real people.
15. The Future: What’s Next in The History of Ransomware
What’s coming?
AI ransomware that negotiates ransom with you.
Ransomware that targets smart homes and cars.
Ransomware that attacks through your smart TV.
Government ransomware. Countries attacking each other.
The history of ransomware is accelerating.
By 2030, ransom payments could hit 20 billion a year.
Be Ready
The history of ransomware shows the next attack is always bigger.
16. Final Thoughts: The History of Ransomware Is About Human Greed
The history of ransomware started with one guy mailing floppies.
Now it’s billion dollar gangs.
It’s not about code. It’s about money.
The history of ransomware proves that as long as there is money and data, there will be criminals.
Your job is to make sure you’re not the easiest target.
Because in the history of ransomware, the easiest target always gets hit first.
Frequently Asked Questions
1. What is the history of ransomware in short
The history of ransomware started in 1989 with AIDS Trojan. It went mainstream in 2013 with CryptoLocker. In 2017 WannaCry hit 300,000 computers. In 2021 Colonial Pipeline was shut down. In 2026 AI ransomware is the new threat.
2. When was the first ransomware attack
The history of ransomware begins in 1989 with the AIDS Trojan. Dr. Joseph Popp mailed floppy disks that locked computers and demanded $189.
3. What is the biggest ransomware attack ever
By damage, NotPetya 2017 at 10 billion dollars. By ransom, 75 million paid in 2024. The history of ransomware shows both keep growing.
4. How much money is made from ransomware
1.1 billion dollars paid in 2024. The history of ransomware shows payments double every 2 years.
5. Who is behind ransomware attacks
The history of ransomware shows 3 groups. Criminal gangs, nation states, and affiliates using Ransomware-as-a-Service.
6. How can I prevent ransomware
Based on the history of ransomware: backups, patching, 2FA, and employee training stop 80% of attacks.
7. What is double extortion
The history of ransomware shows it started in 2020. Hackers steal your data AND encrypt it. So you have to pay even with backups.
8. Will ransomware stop in the future
No. The history of ransomware shows it only gets bigger. As long as there is Bitcoin and data, there will be ransomware.